Architecting Enterprise Storage for the Ransomware Era: Why Convergence and Immutable Storage Matter
There was a time when disaster recovery planning revolved around natural disasters, severed fiber cables, or catastrophic hardware faults. If an unrecoverable failure hit an array, system architects leaned on secondary copies stored on tape or secondary off-site disks. But that paradigm belongs to another era. Today, enterprise storage operates under hostile conditions where adversaries deliberately hunt down snapshot catalogs, shadow copies, and traditional backup volumes before executing encryption payloads.
Recent market analysis confirms an uncomfortable reality: primary storage is no longer collateral damage; it is the target. When cybercriminals breach an infrastructure perimeter, their earliest actions involve crippling recovery capabilities. In response, enterprise IT leaders must transition from passive data retention to an active, resilient architectural model. Achieving true business survival demands unified cyber resilience, behavioral anomaly detection, and rapid recovery engineered directly into the data layer.
The Breakdown of Fragmented Data Protection
Historically, enterprise teams segregated IT responsibilities into silos. Primary storage administrators managed capacity, IOPS, and low-latency workloads. Security teams maintained firewall perimeters and endpoint detection. Backup teams handled nightly replication tasks. This fragmentation created massive operational blind spots, leaving organizations with disjointed tools that take days or weeks to coordinate when an intrusion occurs.
During a coordinated attack, every hour spent verifying whether a restore point is clean translates directly into revenue loss, regulatory liability, and reputational risk. The modern consensus is clear: resilience must be converged. Primary storage, file protocols, and operational recovery workflows need to integrate so that detection triggers defensive behaviors instantly.
When an infrastructure relies on fragmented components, data engineers are left scrambling across siloed consoles. To counter advanced persistent threats, progressive organizations are consolidating structured and unstructured footprints using unified storage architectures that bridge protocol boundaries, enforce unified access governance, and eliminate vulnerable management gaps across hybrid platforms.
The Core Pillar: Native Cyber Resiliency and Immutable Safeguards
Detection alone cannot save a company if write operations remain vulnerable. Attackers frequently dwell inside corporate networks for weeks, escalating privileges and systematically corrupting snapshots before launching extortion routines. If an administrative credential compromise allows malicious actors to wipe backup retention policies, disaster recovery plans crumble.
To build an impervious defense, zero-trust principles must be enforced right down to the disk blocks. This requires hardened, write-once-read-many retention mechanisms that prevent modification or deletion regardless of account permissions. By implementing hardware-enforced and software-attested immutable storage, enterprises guarantee that once a golden image or backup dataset is written, no rogue actor, compromised root credential, or programmatic script can alter it until its predetermined lifecycle policy expires.
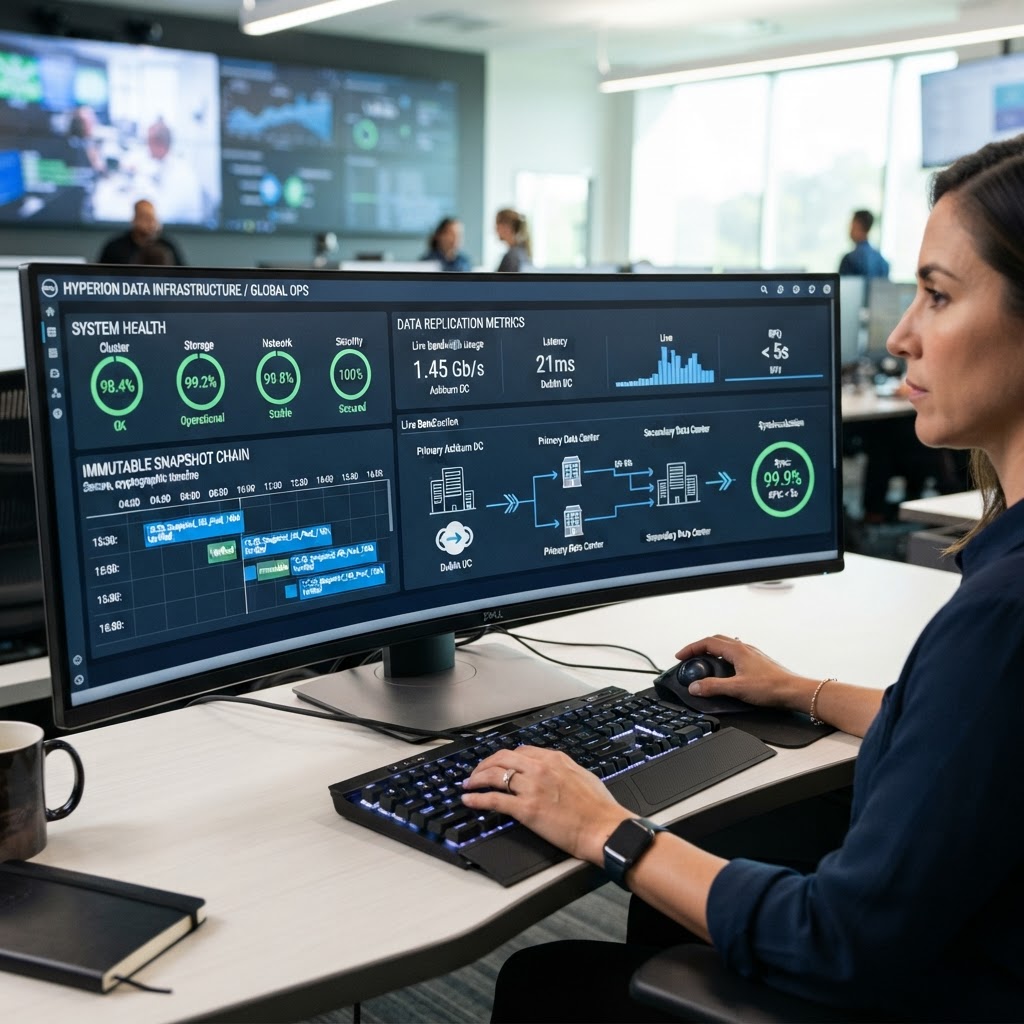 Combining native immutability with micro-snapshots enables zero-footprint point-in-time recovery. Rather than dealing with multi-day copy jobs across the wide area network, organizations can roll back corrupted volumes directly on the storage fabric, reducing Recovery Time Objectives (RTO) from days to minutes.
Integrating Active Detection into the Storage Layer
Storage systems process millions of IOPS per second. They are uniquely positioned to observe the early operational indicators of malicious behavior well before an endpoint antivirus client raises an alarm. Modern cyber-resilient architectures leverage real-time telemetry at the storage fabric to monitor:
- Entropy Shifts: Uncharacteristic spikes in data entropy indicate that plain-text data is being compressed and encrypted on the fly.
- Unusual I/O Velocity: Massive spikes in write, overwrite, and rename commands within directories that typically exhibit static read-dominant behavior.
- Mass File Extension Changes: Automated identification of systemic namespace tampering typical of modern ransomware payloads.
When storage engines identify these behavioral markers, integrated defensive triggers can freeze network mounts, lock out affected identities, and capture immediate, out-of-band immutable snapshots to preserve uncorrupted state vectors for clean forensics and instant restore operations.
Bridging High-Speed Workloads and Mission-Critical Recovery
The ultimate test of any defensive architecture is the speed and integrity of the restore process. Enterprises cannot afford protracted recovery sprints that disrupt customer-facing applications, electronic transaction processing, or analytics pipelines. Resiliency strategies must encompass modern containerized microservices, unstructured data pools, and mission-critical databases simultaneously.
Deploying a robust ransomware protection framework ensures that recovery operations are not just possible, but deterministic. When high-value enterprise assets—from petabyte-scale file repositories to core transactional databases—can be verified against non-repudiable baselines, operational leadership can refuse extortion demands with complete technical confidence.
The Strategic Imperative
Cyber threats are constantly evolving, and regulatory scrutiny around operational resilience and continuous data availability is intensifying worldwide. Treating storage infrastructure as a passive utility is a liability no modern enterprise can afford. By converging proactive anomaly detection, granular access controls, and air-tight immutable recovery into a single architecture, technology leaders turn their storage foundation into their strongest line of defense.